
การประชุมศูนย์ข้อมูลเกษตรแห่งชาติ (NABC) ครั้งที่ 10/2569
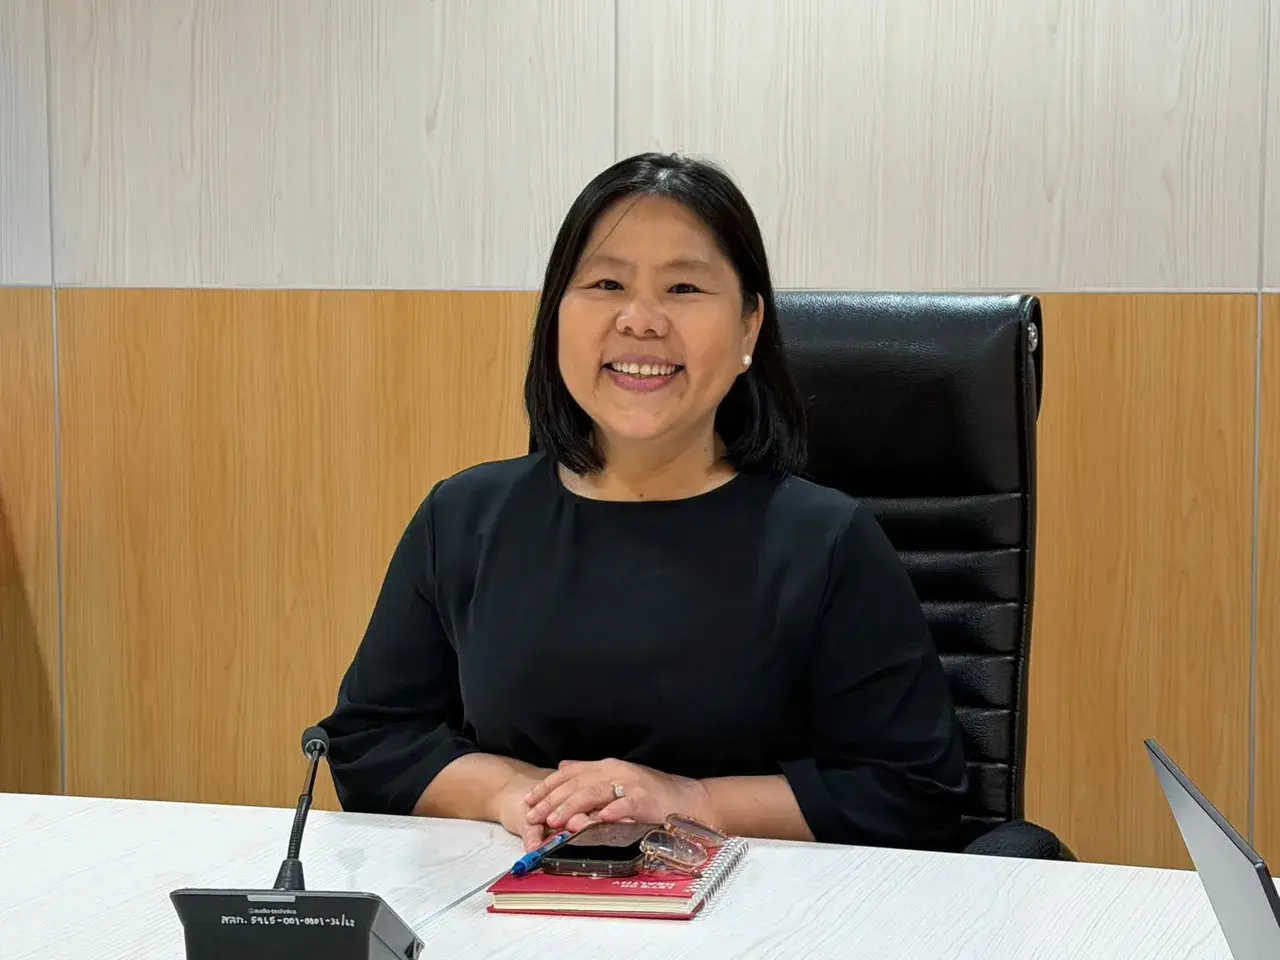
วันที่ 30 ตุลาคม 2569 นายณรงค์ศักดิ์ การันต์ ผู้อำนวยการศูนย์ข้อมูลเกษตรแห่งชาติ มอบหมายให้ นางอารีย์ ธีระดำรงตระกูล ผู้อำนวยการส่วนบริการวิชาการและนวัตกรรมข้อมูลขนาดใหญ่ เป็นประธานการประชุมศูนย์ข้อมูลเกษตรแห่งชาติ ศูนย์ข้อมูลเกษตรแห่งชาติ ครั้งที่ 10/2569 ณ ห้องประชุม 1 ชั้น 3 อาคารนวัตกรรม สำนักงานเศรษฐกิจการเกษตร
การประชุมครั้งนี้เป็นการติดตามและรับทราบผลการดำเนินงานของแต่ละส่วน/ฝ่าย ประจำเดือนตุลาคม 2569 พร้อมรายงานแผนการใช้จ่ายงบประมาณรายจ่ายประจำปีงบประมาณ พ.ศ. 2570 ผลการใช้จ่ายงบประมาณประจำเดือนตุลาคม 2569 และแผนการดำเนินงานโครงการจัดซื้อจัดจ้าง ประจำปีงบประมาณ พ.ศ. 2570 เพื่อให้การดำเนินงานเป็นไปตามแผนงาน
นอกจากนี้ ที่ประชุมยังได้รับทราบและแลกเปลี่ยนข้อมูลเกี่ยวกับ การเตรียมความพร้อมรับมือภัยคุกคาม AI ในองค์กร ตามกรอบมาตรฐาน ISO/IEC 27090:2026 และแนวทางปฏิบัติ AI Security Guidelines ของสำนักงานคณะกรรมการการรักษาความมั่นคงปลอดภัยไซเบอร์แห่งชาติ (สกมช.) โดยให้ความสำคัญกับการทำความเข้าใจภัยคุกคามที่อาจเกิดขึ้นจากการใช้งาน AI การบริหารจัดการความเสี่ยง และการกำหนดมาตรการรักษาความปลอดภัยของข้อมูลและระบบสารสนเทศ เพื่อให้สามารถนำเทคโนโลยี AI มาใช้ในการปฏิบัติงานได้อย่างปลอดภัยและเหมาะสม
On 30 October 2026, Mr. Narongsak Karan, Director of the National Agricultural Big Data Center (NABC), assigned Mrs. Aree Teeradamrongtrakun, Director of Big Data Knowledge and Innovation Service Subdivision, to chair the NABC Meeting No. 10/2026. The meeting was held at Meeting Room 1, 3rd Floor, Innovation Building, Office of Agricultural Economics (OAE).
The meeting reviewed and acknowledged the performance updates of each division for October 2026. It also covered the FY2027 expenditure budget plan, the budget disbursement results for October 2026, and the implementation plan for procurement and procurement-related projects for FY2027 to ensure that operations proceed in accordance with the established plans.
In addition, the meeting acknowledged and exchanged information on organizational preparedness for AI-related threats, in accordance with the ISO/IEC 27090:2026 standard framework and the AI Security Guidelines issued by the National Cyber Security Agency (NCSA). Key areas of focus included understanding potential threats arising from AI usage, risk management, and establishing security measures for data and information systems to ensure that AI technologies can be adopted safely and appropriately in organizational operations.